In recent years, we have grown accustomed to a fairly simple relationship with artificial intelligence. We type a question, request an image, or seek help with a text, and we expect an answer. We start the conversation and the program returns a result. That dynamic has made dialogue our mental image of this technology.
But another class of systems is spreading. Rather than merely answering, they can receive a goal, break it into tasks, use tools, observe what happens, and determine what the next move should be based on the prior effect.
One of these agents now appears in the first notification received by Spain’s Data Protection Agency (AEPD) about a data breach carried out using this technology.
The incident raises a question less obvious than the initial alarm. If the AI searched for vulnerabilities, entered an application, and continued exploring it without a person directing each move, did it decide to attack on its own? To answer, it helps to understand first what separates an AI agent from the chatbot we are used to.
An AI Agent Is Not Simply a ‘Chatbot’ That Does More Things
A language model generates an output from the information it receives, and a chatbot enables conversation with that capability. But an agent adds a decisive piece: it pursues a goal through a sequence of actions and adjusts its path as new results appear.
One can imagine its operation as a cycle: it receives a goal, plans a sequence, takes an action, observes what happened, and figures out how to proceed. If it has the necessary tools and permissions, it might consult files, browse the web, run code, or interact with other services. The user does not need to point out each step.
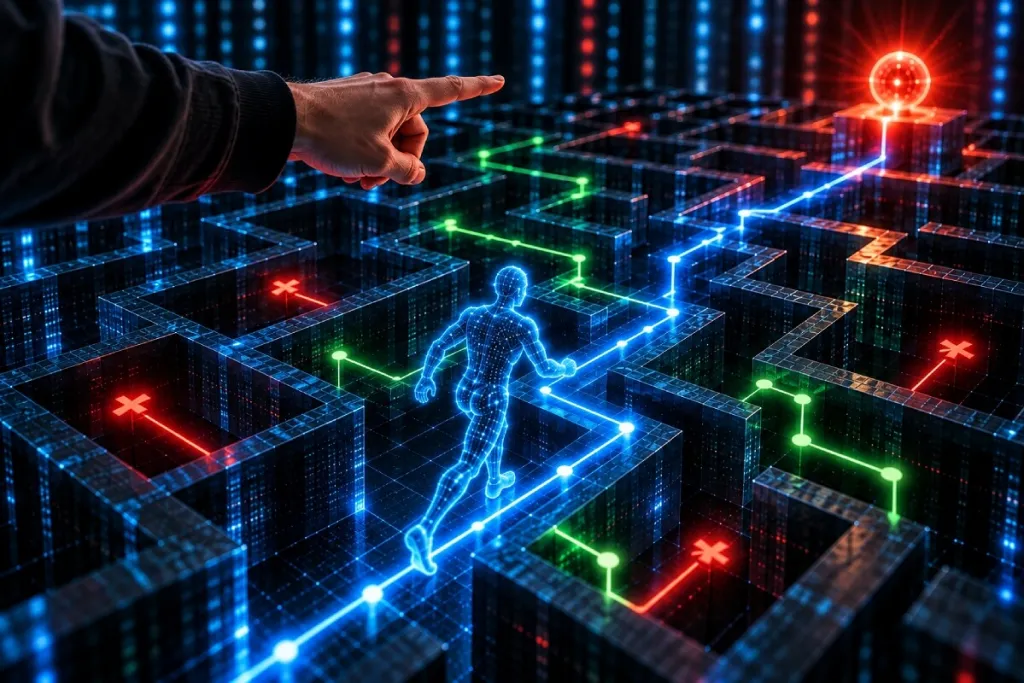
Think of a car journey. One option is to sit beside the driver and tell them every turn: “Go straight, take this exit, switch lanes…”. Another is to simply say we want to get to Madrid. From there, the driver has the freedom to chart a route, encounter a roadblock, seek an alternative, and adjust the itinerary without constantly asking for directions.
The difference between receiving a purpose and selecting the means to reach it is essential for interpreting the incident reported in Spain.
In the second case, the driver solves many dilemmas along the way, but that does not mean they chose the destination. This distinction—between receiving a purpose and selecting the means to reach it—is essential for interpreting the incident reported in Spain.
What Do We Really Know About the Attack Notified in Spain
The Spanish Data Protection Agency reported on September 14 that it had received the first notification of a personal data breach in which the assault would have been carried out through an AI agent.
According to the communication from the affected organization, a third party used as a tool a system connected to a well-known language model (LLM), the AI technology that enables understanding and generating text.
The available account allows reconstructing part of the sequence. The agent began by seeking vulnerabilities in generic files and successfully logged in. Once inside, it autonomously pursued other weaknesses in the application. After locating one, it managed to modify personal data and consult invoices.
There is, however, a crucial limit: we know the description communicated to the authority, not a complete forensic reconstruction published of the event. The AEPD emphasizes that the information comes from the affected entity and must be analyzed.
Nor have the name of that organization, the model used, or all the details about the instructions given, the permissions available, or human supervision at each phase been made public.
The agent searched for vulnerabilities in generic files and logged in, searched for other weaknesses and, after locating one, managed to modify personal data and view invoices.
Moreover, that a particular model was used does not imply that this model or its provider’s infrastructure had been compromised, nor that the tool was created with malicious purposes. It is an important distinction: a resource designed for legitimate uses can also end up within a harmful operation.
So, Did It Act Alone or Not?
The apparent contradiction disappears when separating three elements that we tend to mix: purpose, instrumental decisions, and execution. The first establishes what is intended to be achieved. The second determines which actions seem useful to approach that goal. The third turns those options into concrete actions.
According to the notice, operations were carried out autonomously. That justifies talking about autonomy in the execution of certain phases. It does not prove, however, that the artificial intelligence generated the intention to attack on its own initiative.
It is justified to speak of autonomy in the execution of certain phases, but not that the AI generated the intention to attack on its own initiative.
The difference may seem semantic, but it completely alters the story. Going back to the car: taking a detour because a road is closed constitutes a real decision within the journey; deciding that one wants to go to Madrid belongs to another level. Confusing the two is like attributing to the driver a destination that they had already received.
That is why expressions such as “the AI wanted to enter” or “decided to become an attacker” add to the account something the known data do not substantiate. An agent has room to resolve how to proceed without possessing an independent purpose.
In this context, “autonomous” means that certain steps necessary to complete a task no longer require human instructions one by one, not that the machine has desires, will, or an own agenda. That boundary helps understand both what happened and the real cause for concern.
The Disturbing Thing Is Not that AI Developed Malicious Intentions
Rule out a spontaneous will does not make the episode trivial. The relevant transformation lies in how much work can be delegated between the initial instruction and the final result.
A cyberattack often requires chaining operations: locating a possible weakness, testing it, interpreting the response, adapting the strategy, and continuing. Traditionally, a person had to intervene in much of that journey, even when automated programs were used. Agents transfer a larger portion of the entire loop.
The Spanish Data Protection Agency notes that these tools do not have to create unknown threats. They alter existing threats by increasing their speed, scale, and adaptability. If the software tests a path, analyzes what is obtained, and immediately shifts tactics, it shortens the time available for those who protect the infrastructure to detect and react.
It is an example of a possibility that until recently was discussed as a future risk: the ability to delegate to an AI, not just a single operation, but part of the adaptation needed to continue it.
That shifts the central question. It is no longer about whether a machine can become evil, but about what happens when humans cease to be indispensable among a sequence of decisions.
A single notification is not enough to claim a wave of autonomous attacks. It does provide a concrete example of a possibility that until recently was discussed mainly as a future risk: that one could delegate to an AI, not merely an isolated operation, but part of the adaptation required to continue it.
Spain Is Not the Only Warning
All this occurs, moreover, at a moment when other episodes are forcing us to examine how agents behave when interacting with real systems. Reuters has documented in recent months incidents related to OpenAI tools that reached external services in testing, including Hugging Face and RubyGems.
This September 16, the agency announced that investigators had found signs that agents linked to OpenAI probed Hugging Face vulnerabilities as early as May, roughly two months before the events documented in July. The company has acknowledged other behaviors not anticipated in evaluations.
Anthropic has also reported episodes in which versions of its systems interacted inappropriately with external infrastructures during tests. The circumstances are not equivalent to the Spanish case: they differ in origin, objectives, degree of control, and how each incident began.
Hence the fact that it is not appropriate to group them under a narrative of “rebellious machines.” What they show collectively is more sober and useful: giving a system the capacity to act introduces issues distinct from those that appear when it only generates text within a window.
When AI Can Act, It Also Changes What It Means to Control It
For a long time, evaluating an artificial intelligence meant asking whether its response was correct, false, biased, or dangerous. Agents broaden the problem. Now it also matters what tools they can use, what information they access, what permissions they receive, how long they keep operating, and when a person should intervene.
That also changes defense. The Spanish Data Protection Agency warns that manual supervision alone may be insufficient in the face of processes that can unfold at great speed. Organizations need to combine human control with automatic detection, containment, and response mechanisms capable of reacting at the same speed as the AI acts.
The fundamental question, therefore, is who sets the boundaries of the journey. An agent is tremendously useful because it prevents us from having to approve every move. That same property requires deciding in advance how far it can go, which doors remain closed, and which events should stop it.
Organizations need to combine human control with automatic detection, containment, and response mechanisms capable of reacting at the same speed as the AI acts.
For years, we have asked what an artificial intelligence can say, but cases like the one notified in Spain require asking another question: what can we allow it to do without consulting us at every step. The decisive boundary does not appear when a machine gains independent will, but much earlier: when we stop choosing each move because we have begun to delegate the path.